How It Works
1
Agent tries to email 8,400 customers → Human Signoff pauses it for your review
agent — zsh
user@prod:~$ agent run email-campaign
▸ Drafting email copy... done
▸ Building recipient list... 8,400 contacts
⏸ Paused: send campaign to all customers
Waiting for human signoff_
2
You get a push notification → review context and approve on your phone
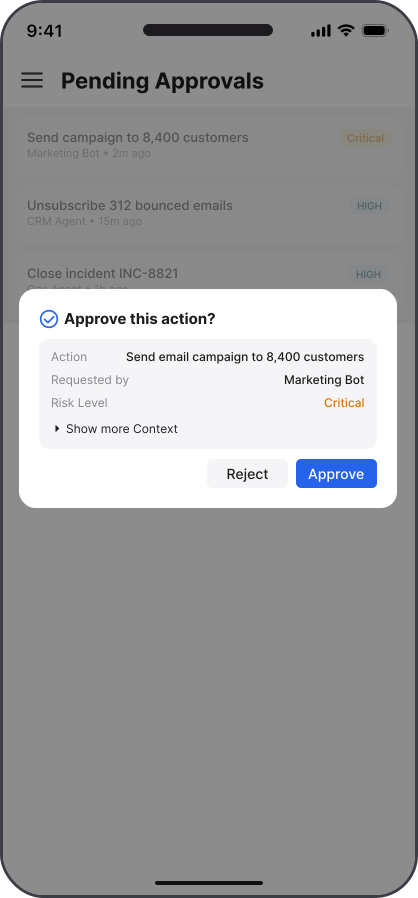
3
Signed by you → action resumes, audit record created
 Human Signoff
/
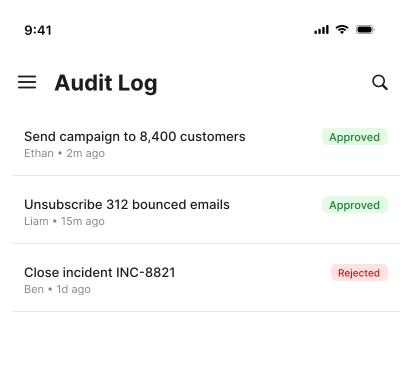
Audit Log
| Time | Action | Context | Requested by | Signer | Result |
|---|---|---|---|---|---|
| 4/15/26 14:03:22 |
Send email campaign to 8,400 customers | Template: Q2 promo — 20% off · 0 external addresses · Immediate send | Marketing Bot | louis@acme.com | ✓ Approved |
| 4/14/26 11:47:05 |
Share internal docs to Slack channel | Document: Q2 Roadmap — Confidential · External channel with 312 members | Marketing Bot | sarah@acme.com | ✓ Approved |
| 4/13/26 09:15:33 |
Delete AWS instances for production | Production · t3.large · Running since Mar 12 · 1 EBS volume (200 GB) | DevOps Bot | louis@acme.com | ✕ Rejected |